
IPv4 access control lists
An ACL is tested line by line and the first match decides, so the same two lines in a different order give the opposite result. A packet that matches nothing is denied at the end. Standard lists match source only and belong near the destination; extended lists match source, destination and protocol. In a wildcard mask, 0 means check. New lines in a numbered list go to the end.
By Arif, founder of Daveth · Updated
The full 11 min walkthrough is in Daveth Pro (Network). See what the plan opens
What this page answers
Does ACL line order matter?
Yes. The switch tests packets against the conditions one by one and the first match decides, so a broad permit before a narrow deny lets the denied range through. Read it in “Two lines, two orders”
How does a wildcard mask work?
A 0 bit means check, the bit must match; a 1 bit means ignore. So 172.20.128.64 0.0.0.31 matches 172.20.128.64 to .95. Read it in “Reading the mask”
Where does a new line go in a numbered ACL?
At the end. After you create an ACL, any additions are placed at the end of the list, so a new deny after an existing permit never matches. Read it in “Adding a line, and where it lands”
Two lines, two orders
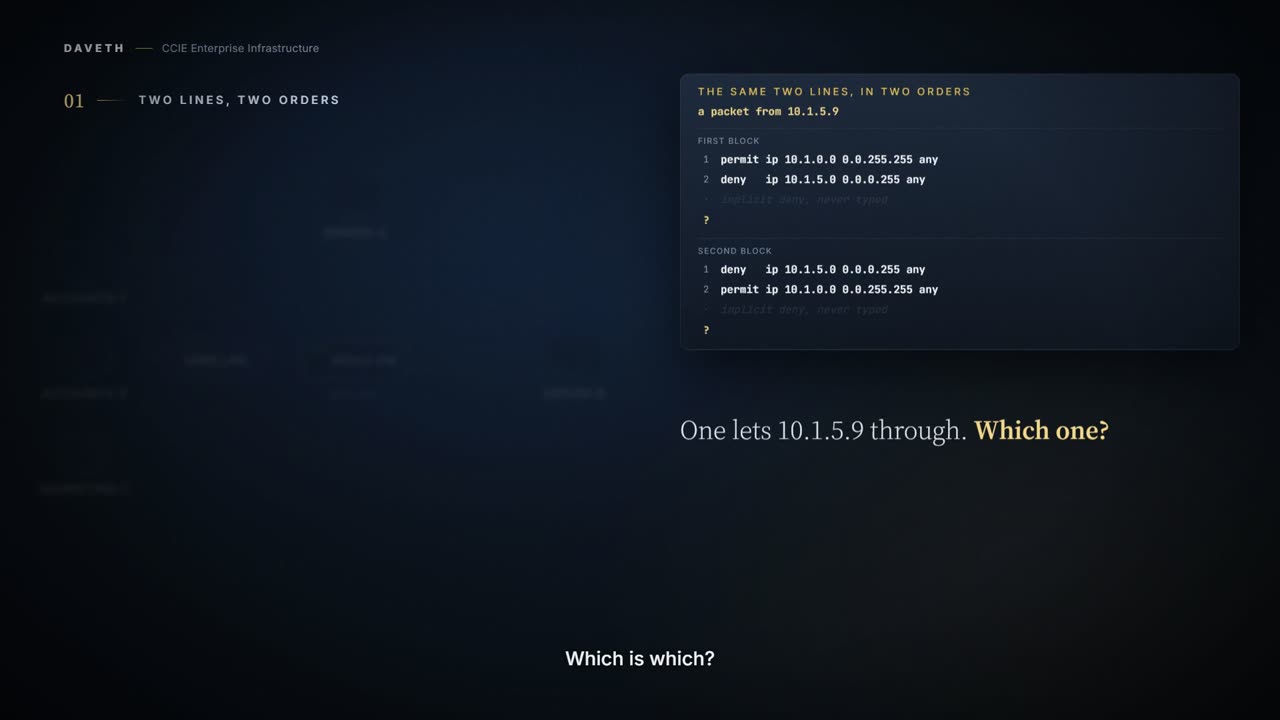
Same two lines, twice, in different orders:
permit ip 10.1.0.0 0.0.255.255 any
deny   ip 10.1.5.0 0.0.0.255 any
deny   ip 10.1.5.0 0.0.0.255 any
permit ip 10.1.0.0 0.0.255.255 any
One of them lets 10.1.5.0/24 through. The other stops it. Work out which before reading on.
An ACL is a sequential collection of permit and deny conditions that apply to packets. One by one, it tests packets against the conditions in an access list. The first match decides whether the switch accepts or rejects the packets. Because the switch stops testing after the first match, the order of conditions in the list is critical.
In the first block a packet from 10.1.5.9 meets the permit for 10.1.0.0/16 first, matches, and testing stops. The deny below it never runs, for any packet. In the second block the deny comes first and catches it. The general ACL guide says it without an example:
The same permit or deny statements specified in a different order can result in a packet being passed under one circumstance and denied in another circumstance.
What happens at the bottom
Now a packet that matches nothing at all, say from 192.168.1.1, in either block:
If no conditions match, the switch rejects the packet. When creating an ACL, remember that, by default, the end of the ACL contains an implicit deny statement for all packets that it did not find a match for before reaching the end.
So neither block "does nothing" to traffic from outside 10.1.0.0/16: both deny it, at the end. An access list with one permit line has not permitted one thing; it has denied everything else. The general guide draws the consequence:
An access list must contain at least one permit statement or all packets are denied entry into the network.
Hold that. Before the end of this page it gets turned upside down.
What each kind can see, and where it belongs
Standard IP access lists use source addresses for matching operations. Extended IP access lists use source and destination addresses for matching operations and optional protocol-type information for finer granularity of control. The switch supports IPv4 standard and extended access lists, numbers 1 to 199 and 1300 to 2699.
Source only, against source, destination and protocol. That decides where each belongs, and the general guide says so:
Because standard access lists test source addresses, they are very efficient at blocking traffic close to a destination. Extended access lists are good for blocking traffic anywhere.
The walk that goes with this page runs on the 17.9 chapter's own example, a small office where only Accounting may reach the payroll server:
This example uses a standard ACL to filter traffic coming into Server B from a port, permitting traffic only from Accounting’s source addresses 172.20.128.64 to 172.20.128.95.
Its fix is a standard list, and notice where it goes: out on Port 1, the port facing Server B, right next to the destination. Put the same one-line list inbound on the users' port and it would stop Marketing reaching Server A too, because a standard list cannot tell the two servers apart.
Configuration: the chapter's fix, on this page's switch.
OFFICE-SW# configure terminal
OFFICE-SW(config)# access-list 6 permit 172.20.128.64 0.0.0.31
OFFICE-SW(config)# interface gigabitethernet1/0/1
OFFICE-SW(config-if)# ip access-group 6 out
OFFICE-SW(config-if)# end
Does list 6 exist on the switch, and what does it hold, in what order? The chapter's own output answers that:
Reproduced line for line: the chapter's show access-lists for list 6, with its Device prompt.
Device# show access-lists
Standard IP access list 6
    10 permit 172.20.128.64, wildcard bits 0.0.0.31
Reading the mask
A wildcard mask bit 0 means check the corresponding bit value; they must match. A wildcard mask bit 1 means ignore that corresponding bit value; they need not match.
Zero means check, one means ignore, the inverse of a subnet mask. So 172.20.128.64 0.0.0.31 checks the first 27 bits and ignores the last five: 172.20.128.64 to .95, Accounting exactly. Two shorthands, and what a standard entry assumes when you give no mask:
The keyword any as an abbreviation for source and source-wildcard of 0.0.0.0 255.255.255.255. The keyword host as an abbreviation for source and source-wildcard of source 0.0.0.0. With standard access lists, if you omit the mask from an associated IP host address ACL specification, 0.0.0.0 is assumed to be the mask.
Work one before moving on. Does 10.1.0.0 0.0.255.255 include 10.1.5.9? That is the arithmetic the opening turned on.
Adding a line, and where it lands
Back to the office. ACCT-2, 172.20.128.75, has to be cut off from payroll, and the engineer adds one line to list 6:
OFFICE-SW# configure terminal
OFFICE-SW(config)# access-list 6 deny 172.20.128.75
OFFICE-SW(config)# end
ACCT-2 still reaches payroll. The chapter says where the new line went:
After you create an ACL, any additions are placed at the end of the list. You cannot selectively add ACL entries to a specific ACL.
It says it more strongly of numbered extended lists:
When you are creating ACEs in numbered extended access lists, remember that after you create the ACL, any additions are placed at the end of the list. You cannot reorder the list or selectively add or remove ACEs from a numbered list.
The new line is below the permit for the /27, which ACCT-2 matches first. The change is accepted, the list shows it, and it can never run. Taking it back out of a numbered list is worse:
You cannot delete an entry from a numbered access list; trying to do so will delete the entire access list.
This is where the two Cisco pages differ, and the page will not pretend otherwise. The 17.9 chapter above says you cannot add an entry in a chosen place, and gives this as the named list's advantage:
The advantage of using named ACLs instead of numbered lists is that you can delete individual entries from a named list.
The general ACL guide describes sequence numbers that do exactly what the chapter says you cannot:
This feature allows users to add sequence numbers to access list entries and resequence them. When you add a new entry, you specify the sequence number so that it is in a desired position in the access list. You can reorder statements in or add statements to a named access list.
And the 17.9 chapter itself heads a section IP Access List Entry Sequence Numbering and notes, of the display:
Starting from the Cisco IOS XE Bengaluru 17.5.1 release, when using the show ip access-list acl_name or the show run section acl_name command, the ACEs are displayed in ascending order according to their sequence numbers.
The walk takes the route both pages support: build a new named list in the right order, then point the interface at it. One list per interface per direction, so the new one replaces list 6:
Only one access list per interface, per protocol, and per direction is allowed.
Configuration: PAYROLL-OUT, in the chapter's named-list form.
OFFICE-SW# configure terminal
OFFICE-SW(config)# ip access-list standard PAYROLL-OUT
OFFICE-SW(config-std-nacl)# deny 172.20.128.75
OFFICE-SW(config-std-nacl)# permit 172.20.128.64 0.0.0.31
OFFICE-SW(config-std-nacl)# deny any
OFFICE-SW(config-std-nacl)# exit
OFFICE-SW(config)# interface gigabitethernet1/0/1
OFFICE-SW(config-if)# ip access-group PAYROLL-OUT out
OFFICE-SW(config-if)# end
Now ACCT-2 stops at line 1, ACCT-1 passes at line 2, and MKT-1 stops at line 3, the explicit deny any. List 6 still exists, applied nowhere. Why write a deny the list already has implicitly? The general guide's reason is the count:
Although all access lists end with an implicit deny statement, we recommend use of an explicit deny statement (for example, deny ip any any). Only packets denied by explicit deny statements are counted, which is why the explicit deny statement will yield more complete data for you.
Continue the lesson
The whole lesson, with its drawings and its questions. 6 more sections after the ones above.